Sometimes you read about cyber attacks and think that something like this couldn't happen to you - until it does. Just such a case occurred recently. The attack vividly demonstrates how social engineering works and how even a rather inexperienced attacker could cause considerable damage.
In a recent case, we tried to reconstruct the attacker's activities on an ESXi hypervisor. The logs available on the system were very limited, which made it difficult to analyze the attacker's activities. The ESXi hypervisor in particular offers detailed logs that can be used for forensic analysis if configured accordingly. The topic of forensic readiness in general was covered in a previous article, which is highly recommended reading. This article focuses on hypervisors, the risks they are exposed to and how to protect them.
Forensic readiness refers to a company's ability to carry out digital forensics efficiently. Every incident is a stressful situation for everyone involved. A high degree of maturity in forensic readiness can shorten the analysis time of incidents and increase the quality of statements about the incident.
The EU Parliament's Digital Operational Resilience Act (DORA) came into force on January 16, 2023. This regulation aims to standardize the risk management for information and communication technologies (ICT) of European financial institutions and thus strengthen the resilience of these organizations against digital threats. Financial institutions and other affected companies have until January 17, 2025 to fully implement the requirements of DORA.
A cyber defense analyst plays a critical role in the field of cyber security.
They help organizations protect their digital systems and networks from cyberattacks and other security breaches.
They also help to improve security policies and procedures to prevent future attacks.
One of these specialists at SECUINFRA is Özgür Bagdemir, who joined SECUINFRA in 2022.
Özgür describes himself as a "cyber security enthusiast" and answers a few questions about his challenging job here.
Companies and organizations operating in the critical infrastructure sector (KRITIS) are subject to special requirements. The BSI Law obliges them to regulate the protection of these critical infrastructures at IT level. SECUINFRA has produced a white paper as a guide and orientation aid to help affected companies with implementation. This guide is available here as a free download.
In this article about the dynamic world of cyber deception, you will learn how dangerous attackers can be made visible with little effort. Using an example implementation and its connection to a SIEM system, we also show how knowledge of previously unknown attacks and attack patterns can be incorporated into the defense and strengthen cyber resilience.
Various tools are used to detect IT security incidents within an organization. The foundation for this is the combination of Endpoint Detection and Response (EDR) and Network Detection and Response (NDR) systems.
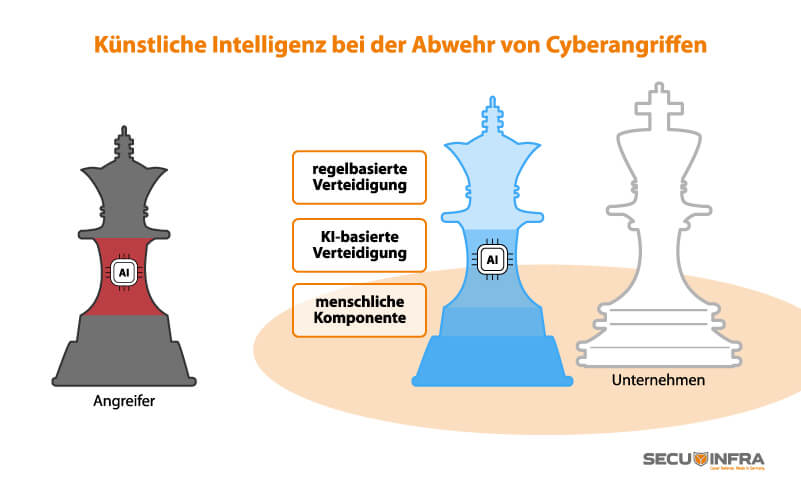
Artificial intelligence is a much-discussed topic. It offers great opportunities, but obviously also harbors risks. And it also has two faces when it comes to IT security.
There are some beliefs, half-truths and myths - and not just in IT - that persist for an astonishingly long time. If they affect the security of a company, it becomes dangerous.