Here you will find articles on the latest findings and in-depth analyses in the field of IT security, presenting both current trends and the in-depth expertise of our cyber defense experts. Immerse yourself in the world of cyber security, enrich your knowledge and stay at the forefront of technological progress.
When the European Central Bank sent a letter to the CEOs of the institutions it supervises on July 7, 2026, its message was clear: Under the title “Addressing AI-enabled cybersecurity threats,” the ECB requires institutions to seriously and demonstrably address AI-enabled cybersecurity threats and to submit an action plan to their respective Joint Supervisory Teams by October 31, 2026.
On August 7, 2026, Fox News published an article with the sensational headline “Russian hackers can steal emails without a click.” It sounds like clickbait, but technically speaking, it’s hardly that. Because that’s exactly the point of the article.
LAUNDRY BEAR, a Russian, state-sponsored hacking group whose latest campaign doesn’t even require a click on a malicious link anymore. All they need is for you to open an email.
Cyberattacks on hospitals are a prime example of how vulnerable critical infrastructure has become. Unlike in many other industries, these attacks can have not only economic consequences but also potentially direct impacts on human lives.
A call from the CEO requesting urgent payment approval. A video conference with familiar faces. A voice message from a colleague asking for quick assistance. For a long time, these very forms of communication were considered trustworthy. But with the advancement of generative AI, the reality of digital communication is changing fundamentally.
Security Operations Centers are under immense pressure. The number of security-related incidents is rising steadily, while there is a shortage of qualified analysts. At the same time, IT environments are becoming more complex, hybrid, and dynamic.
Many companies are therefore investing in additional security tools. But this is precisely where a common misconception arises: More technology does not automatically mean greater security.
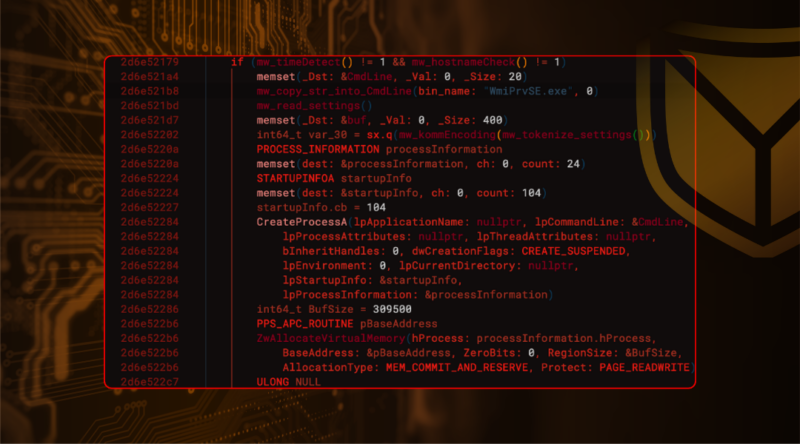
As part of an incident response operation, the SECUINFRA Falcon team identified an interesting malware sample codenamed "CommieLoader" masquerading as an application form.
CommieLoader installed a Cobalt Strike Beacon, which was used by the attacker for command-and-control communication
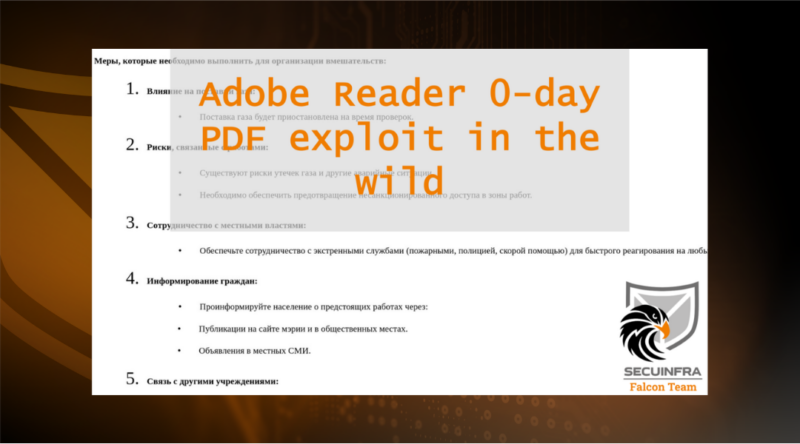
In March 2026, a previously unknown zero-day exploit was discovered in Adobe Reader that is being actively exploited via a specially crafted PDF document. Building on the initial findings of security researcher Haifei Li, this article provides a detailed analysis of the technical structure and functionality of the malicious PDF. It reveals a highly obfuscated attack chain featuring sophisticated obfuscation techniques, fingerprinting mechanisms, and unusual command-and-control communication via RSS feeds.
Alertness and vigilance are crucial in cybersecurity. When repeating this truism, most of us think about social engineering attacks and educating the user how to recognize a phishing mail or a scam call. However, an attentive user can also provide valuable insights on a more technical aspect.
A recent incident response case was started, when the user noticed „strange black windows” on the desktop and took screenshots of them. This was accompanied by PayPal transfers from the user’s account, not authorized by the user.
The incident showcased in this article was detected by the SECUINFRA Cyber Detection & Response Center (CDRC) as part of an MDR alert. The Falcon Team contributed relevant findings about the malware for handling and mitigation. This case serves as a good example of a complex "Clickfix"-style attack chain with steganographic elements.
In today's rapidly evolving digital world, cyber threats are becoming increasingly sophisticated. An incident response plan is no longer an option, but a fundamental necessity. Many organizations rely on Managed Security Service Providers (MSSPs) to secure their operations, but it's important to recognize that outside expertise alone is not enough to eliminate all gaps in incident response.
Modern EDR or XDR solutions are capable of detecting suspicious behavior. The widely used Elastic solution has integrated this feature with Elastic Defend since 2019 and offers industry-leading transparency. Below we show how security experts work with it.
Due to its typical division into IT and OT, the manufacturing industry is a worthwhile target for blackmailers. An overview of specific challenges and recommendations on how production companies can protect sensitive data and failure-critical processes.