Monitor systems securely and detect cyberattacks early
Protect production facilities, industrial processes, and critical infrastructure with state-of-the-art OT security monitoring, and integrate your OT security into a comprehensive Security Operations Center.
Increasing digitalization (Industry 4.0, IIoT) and the convergence of IT and OT are opening up new entry points for cybercriminals. Outdated legacy systems and insecure industrial protocols require the use of specialized OT monitoring solutions.
Visibility: Raising Awareness
Centralized asset and vulnerability management provides transparency into the OT system landscape and forms the basis for a traceable assessment of the security posture.
Detection: Identifying Threats Early
Specialized OT monitoring, integrated with a central SIEM, detects anomalies and attacks without disrupting ongoing operations. A particular focus is placed on the interplay between cybersecurity and safety.
Response: Prepared and Ready to Act in an Emergency
An OT SOC with well-established escalation procedures and playbooks initiates coordinated measures before a cyber incident leads to an operational outage or cyber-physical damage.
Focus on Regulatory Requirements
The core components of an effective attack detection system are asset inventory, the detection of anomalies in OT and IT, and analysis by specialized SOC analysts.
NIS-2: The directive significantly expands the scope of affected companies while simultaneously tightening cybersecurity requirements. OT and IT monitoring form the core of effective risk management, which includes strict reporting requirements.
BSIG, EnWG, and TKG: Energy suppliers and telecommunications providers are required to operate intrusion detection systems (IDS/SzA).
The BSI Basic Protection and B3Sprovide the framework for deriving measures, determining the maturity level, and evaluating the state of the art.
A holistic view of OT environments alongside IT systems is the key to an effective cyber defense strategy.
David Bischoff, Head of Cyber Defense Consulting
David Bischoff, Head of Cyber Defense Consulting
SECUINFRA BEST PRACTISE
IT and OT: A Shared Operational Picture
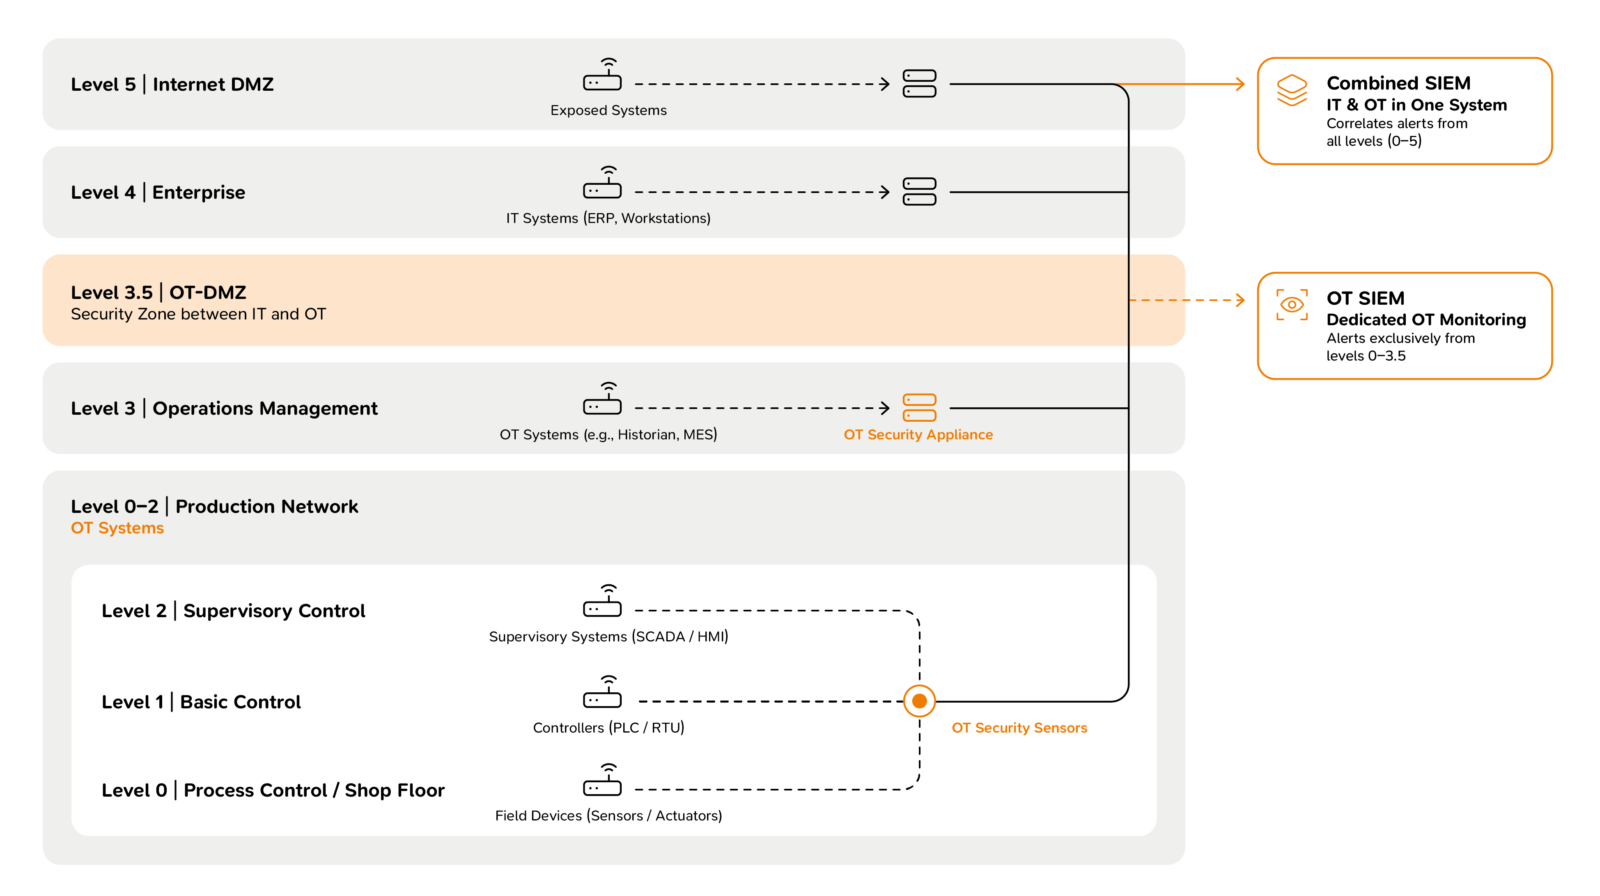
Cyberattacks do not stop at the network boundary with the OT DMZ. We consolidate telemetry from IT and OT environments into a central SIEM. This makes attack paths fully traceable and enables a precise response.
THE TECHNICAL BASIS
What does modern OT security monitoring entail?
OT security solutions that specialize in specific areas combine passive network monitoring with asset inventory and exposure management. This allows anomalies to be detected in real time without disrupting ongoing operations.
Asset Discovery & Inventory
Vulnerability Management
Network Monitoring & Anomaly Detection
Security Monitoring
Incident Response
A RELIABLE PARTNER
We are your partner for IT and OT security
Complex IT/OT architectures, strict regulatory requirements, specialized in cyber defense: We combine experience with technical know-how from both worlds.
All under one roof: We are your partner for cyber defense consulting and monitoring of IT and OT SOCs.
Vendor-neutral: Technology consulting that focuses on your environment, not on products.
Tailored to the environment: customizable MDR services for customers.
Experience in a regulated environment: Proven experience in highly regulated critical infrastructure.
Specializing in Cyber Defense: In-house, experienced SOC engineers and analysts for IT and OT.
Strategic SOC Consulting & Tool Selection
We develop a SOC strategy that integrates IT and OT security and is tailored to your operations. We provide vendor-neutral support to help you select, integrate, and optimize the right OT security solutions.
SIEM and SOC Integration
We help you integrate log data and alerts from your OT and IT environments into a central SIEM. In addition, we develop dedicated use cases for company-wide detection of cyberattacks.
MDR Services
With our MDR services, we continuously monitor your OT and IT environments to detect and assess attacks. When necessary, we respond quickly and effectively.
OT Forensics and Incident Response
In the event of an emergency, our forensic experts work with your operations managers to coordinate all necessary measures—from ensuring business continuity to analyzing the attack path and facilitating a controlled recovery.
Partners
We provide vendor-neutral consulting and draw on a portfolio of strategic technology partners. This enables us to implement the right solution for every OT environment.
FREQUENTLY ASKED QUESTIONS
Expert Answers on OT Security & SzA
Learn more about the technical and regulatory foundations of industrial cyber defense.
No, because OT security monitoring is primarily based on passive network monitoring. This involves monitoring and analyzing network traffic without interfering with control processes. There is no need to install agents on the systems or send active queries to them. Nevertheless, it is possible to use minimally invasive active monitoring mechanisms as a supplement to optimize cyber defense capabilities.
That depends on the sector, company size, and classification. Operators of critical infrastructure are required to use intrusion detection system (IDS/SzA). Companies classified as important or particularly important facilities under NIS-2 must demonstrate effective risk management, which includes OT monitoring. We can help you determine your classification.
In its guidance document (OH SzA), the BSI identifies three areas: logging, detection, and response. In practice, these also include asset inventory, anomaly detection in OT and IT, and assessment by specialized SOC analysts.
A SIEM centrally aggregates events from IT and OT and enables company-wide correlation of security-related events. When combined with a specialized OT monitoring solution, it forms the foundation for attack detection. We can assist you with integration into existing SIEM systems and, if necessary, advise you on the appropriate solution.
Cyber-physical security prevents cyberattacks on control systems from causing physical damage, such as excess pressure in tanks, valves opening uncontrollably, or air conditioning failure. This protects people, the environment, and facilities.
By using additional sensors, attacks outside of network traffic can be detected. Examples include monitoring the radio spectrum for interference signals, detecting drones in the vicinity of facilities, and detecting tampering with devices and control cabinets.