

Content
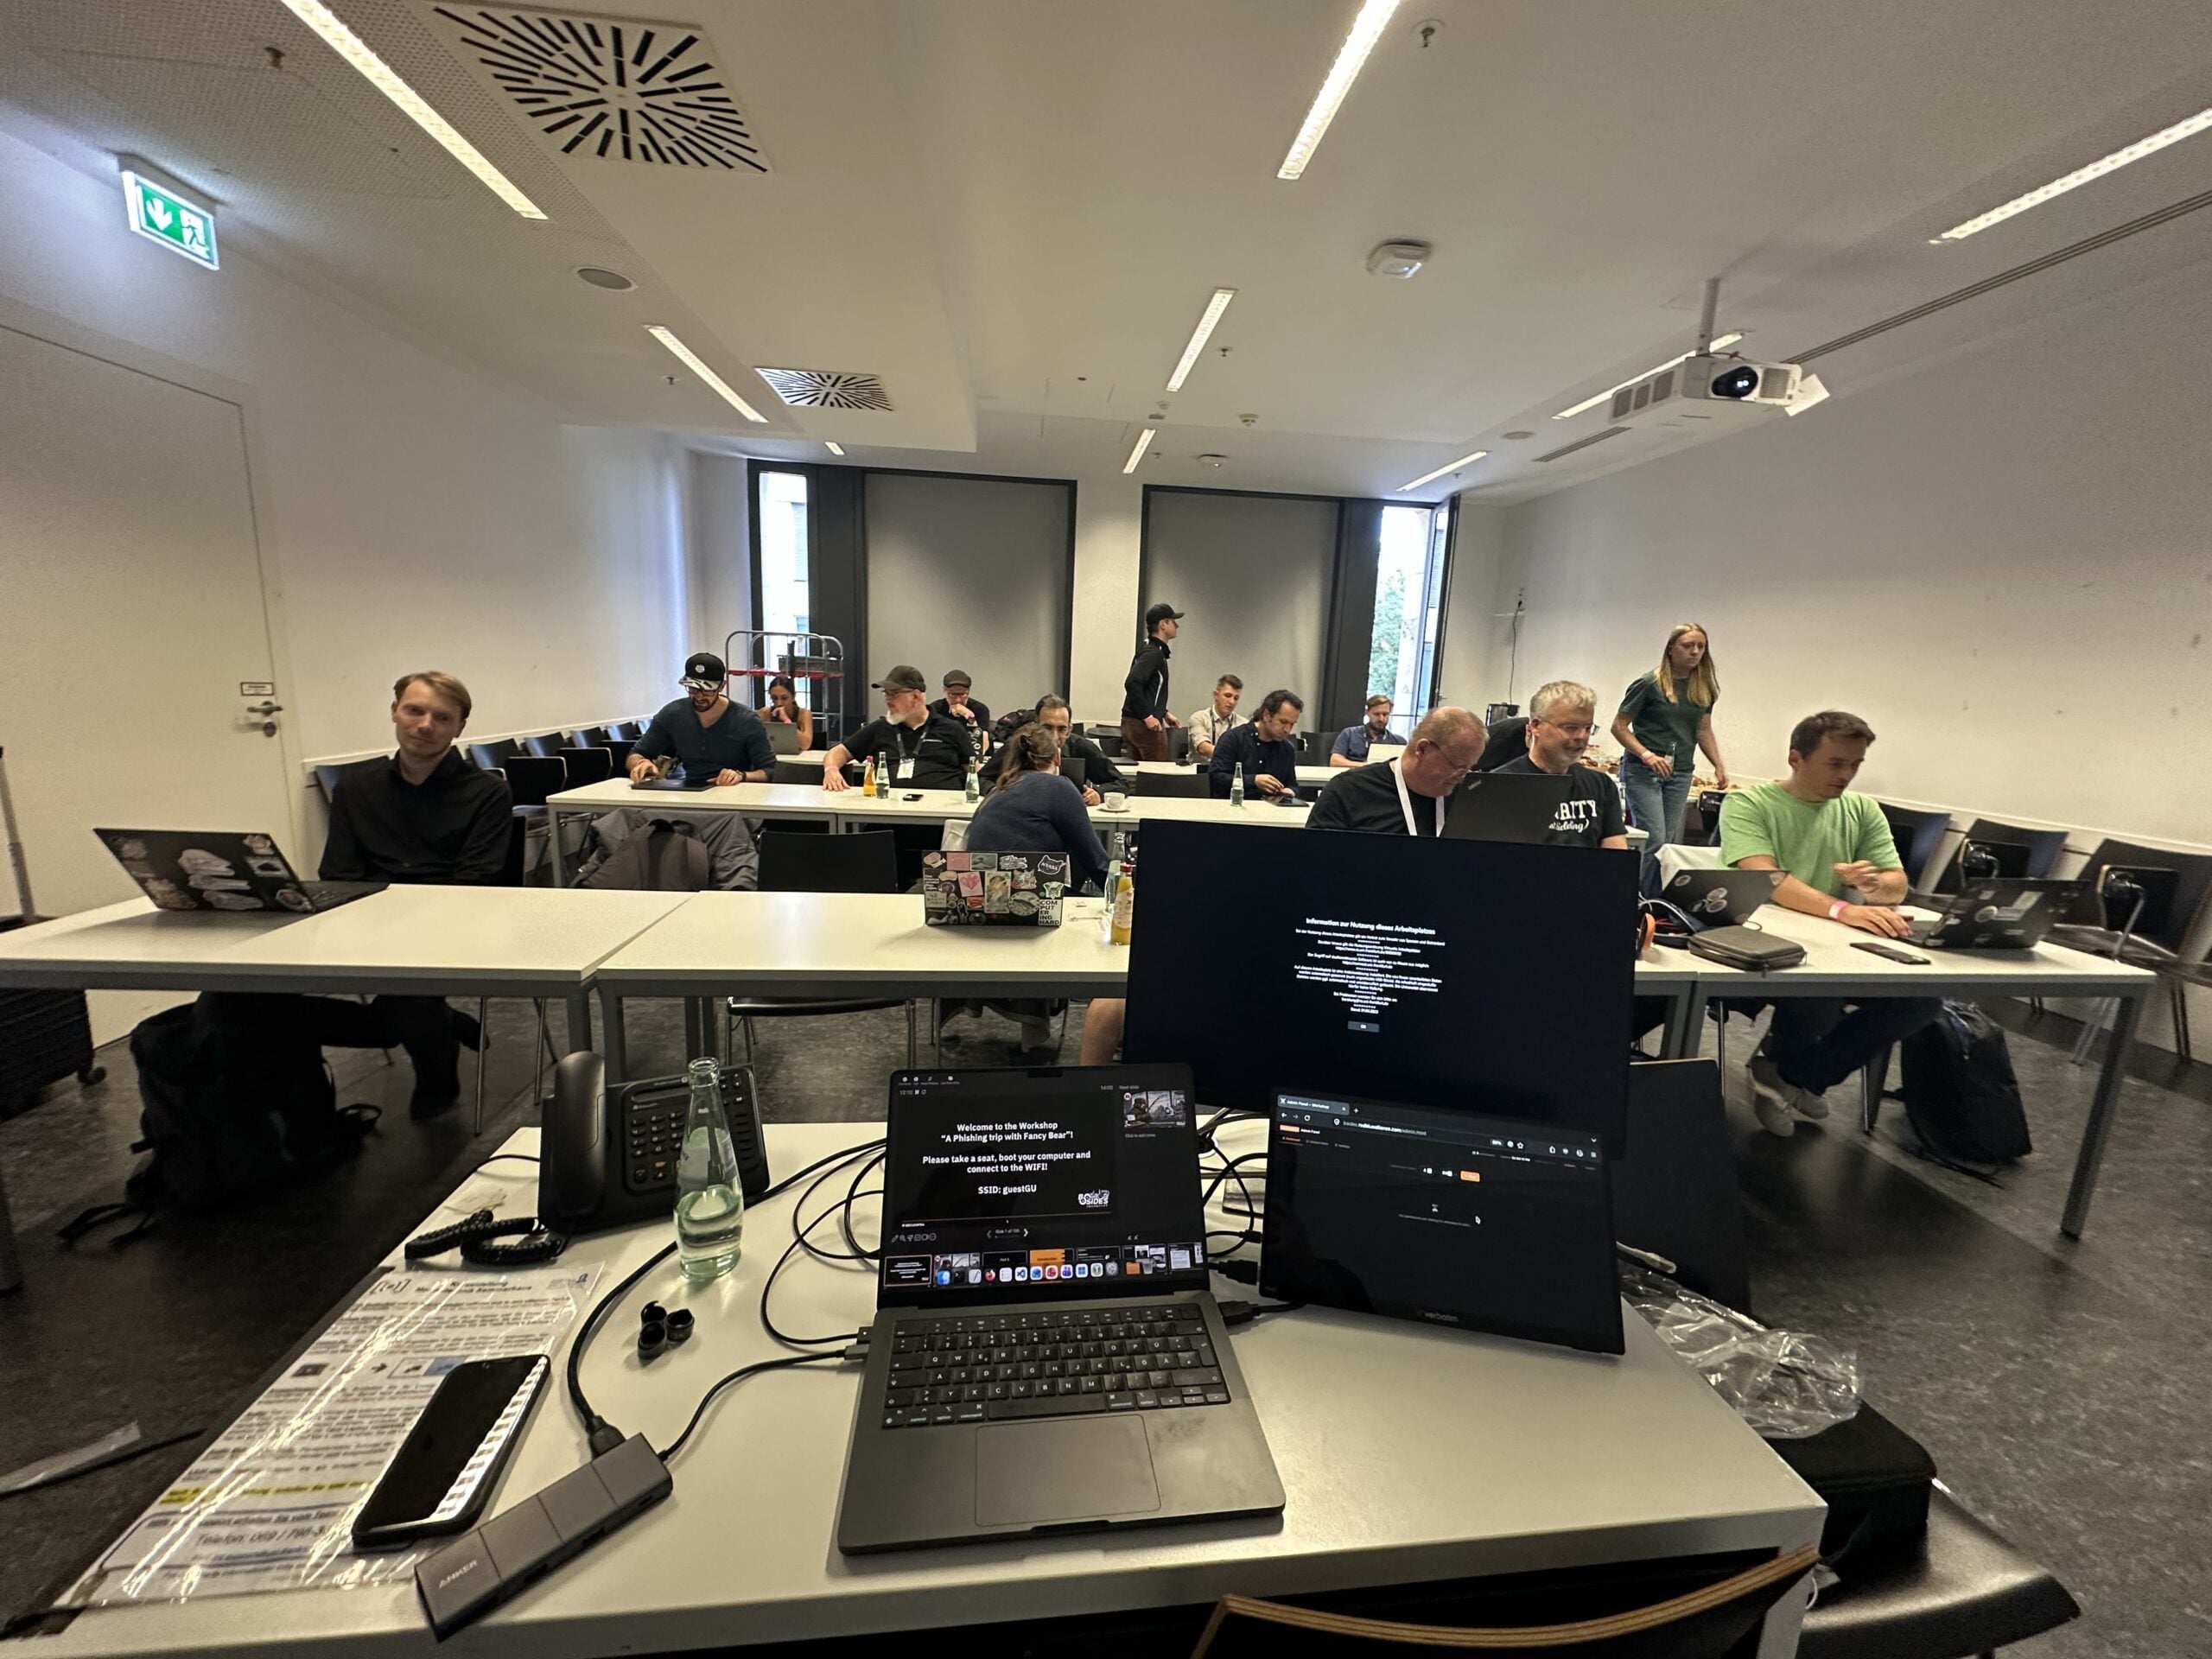
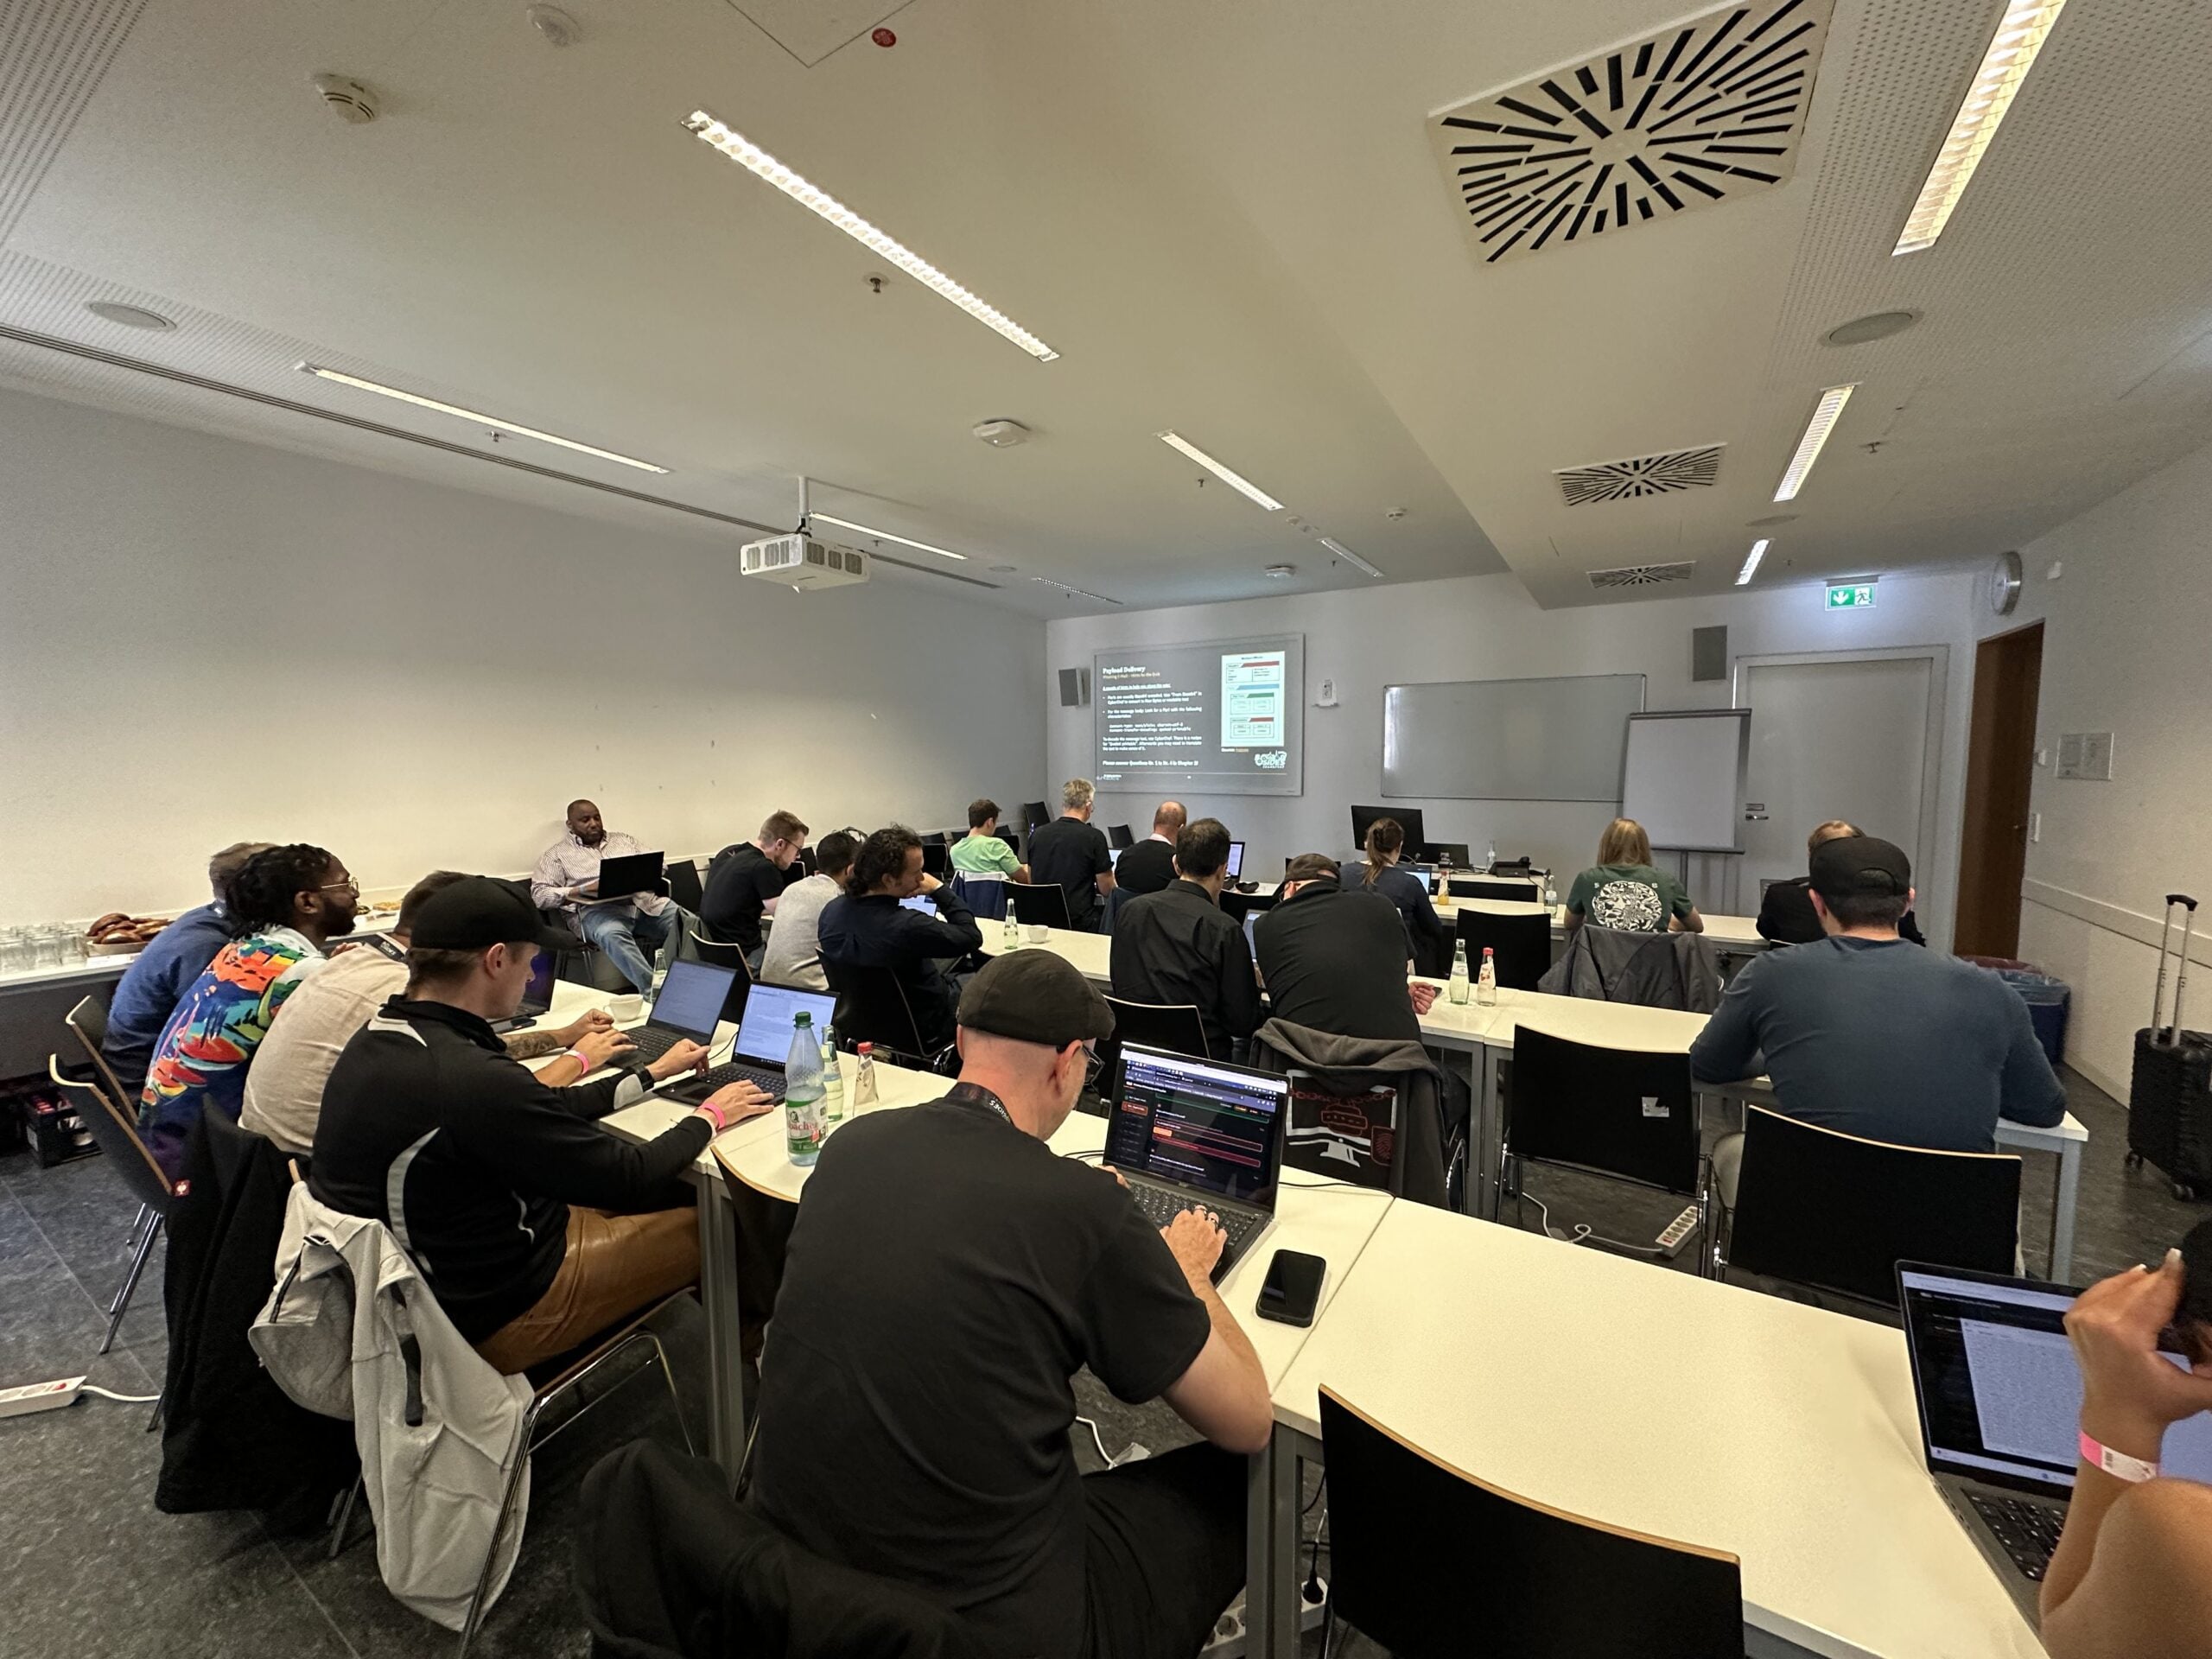
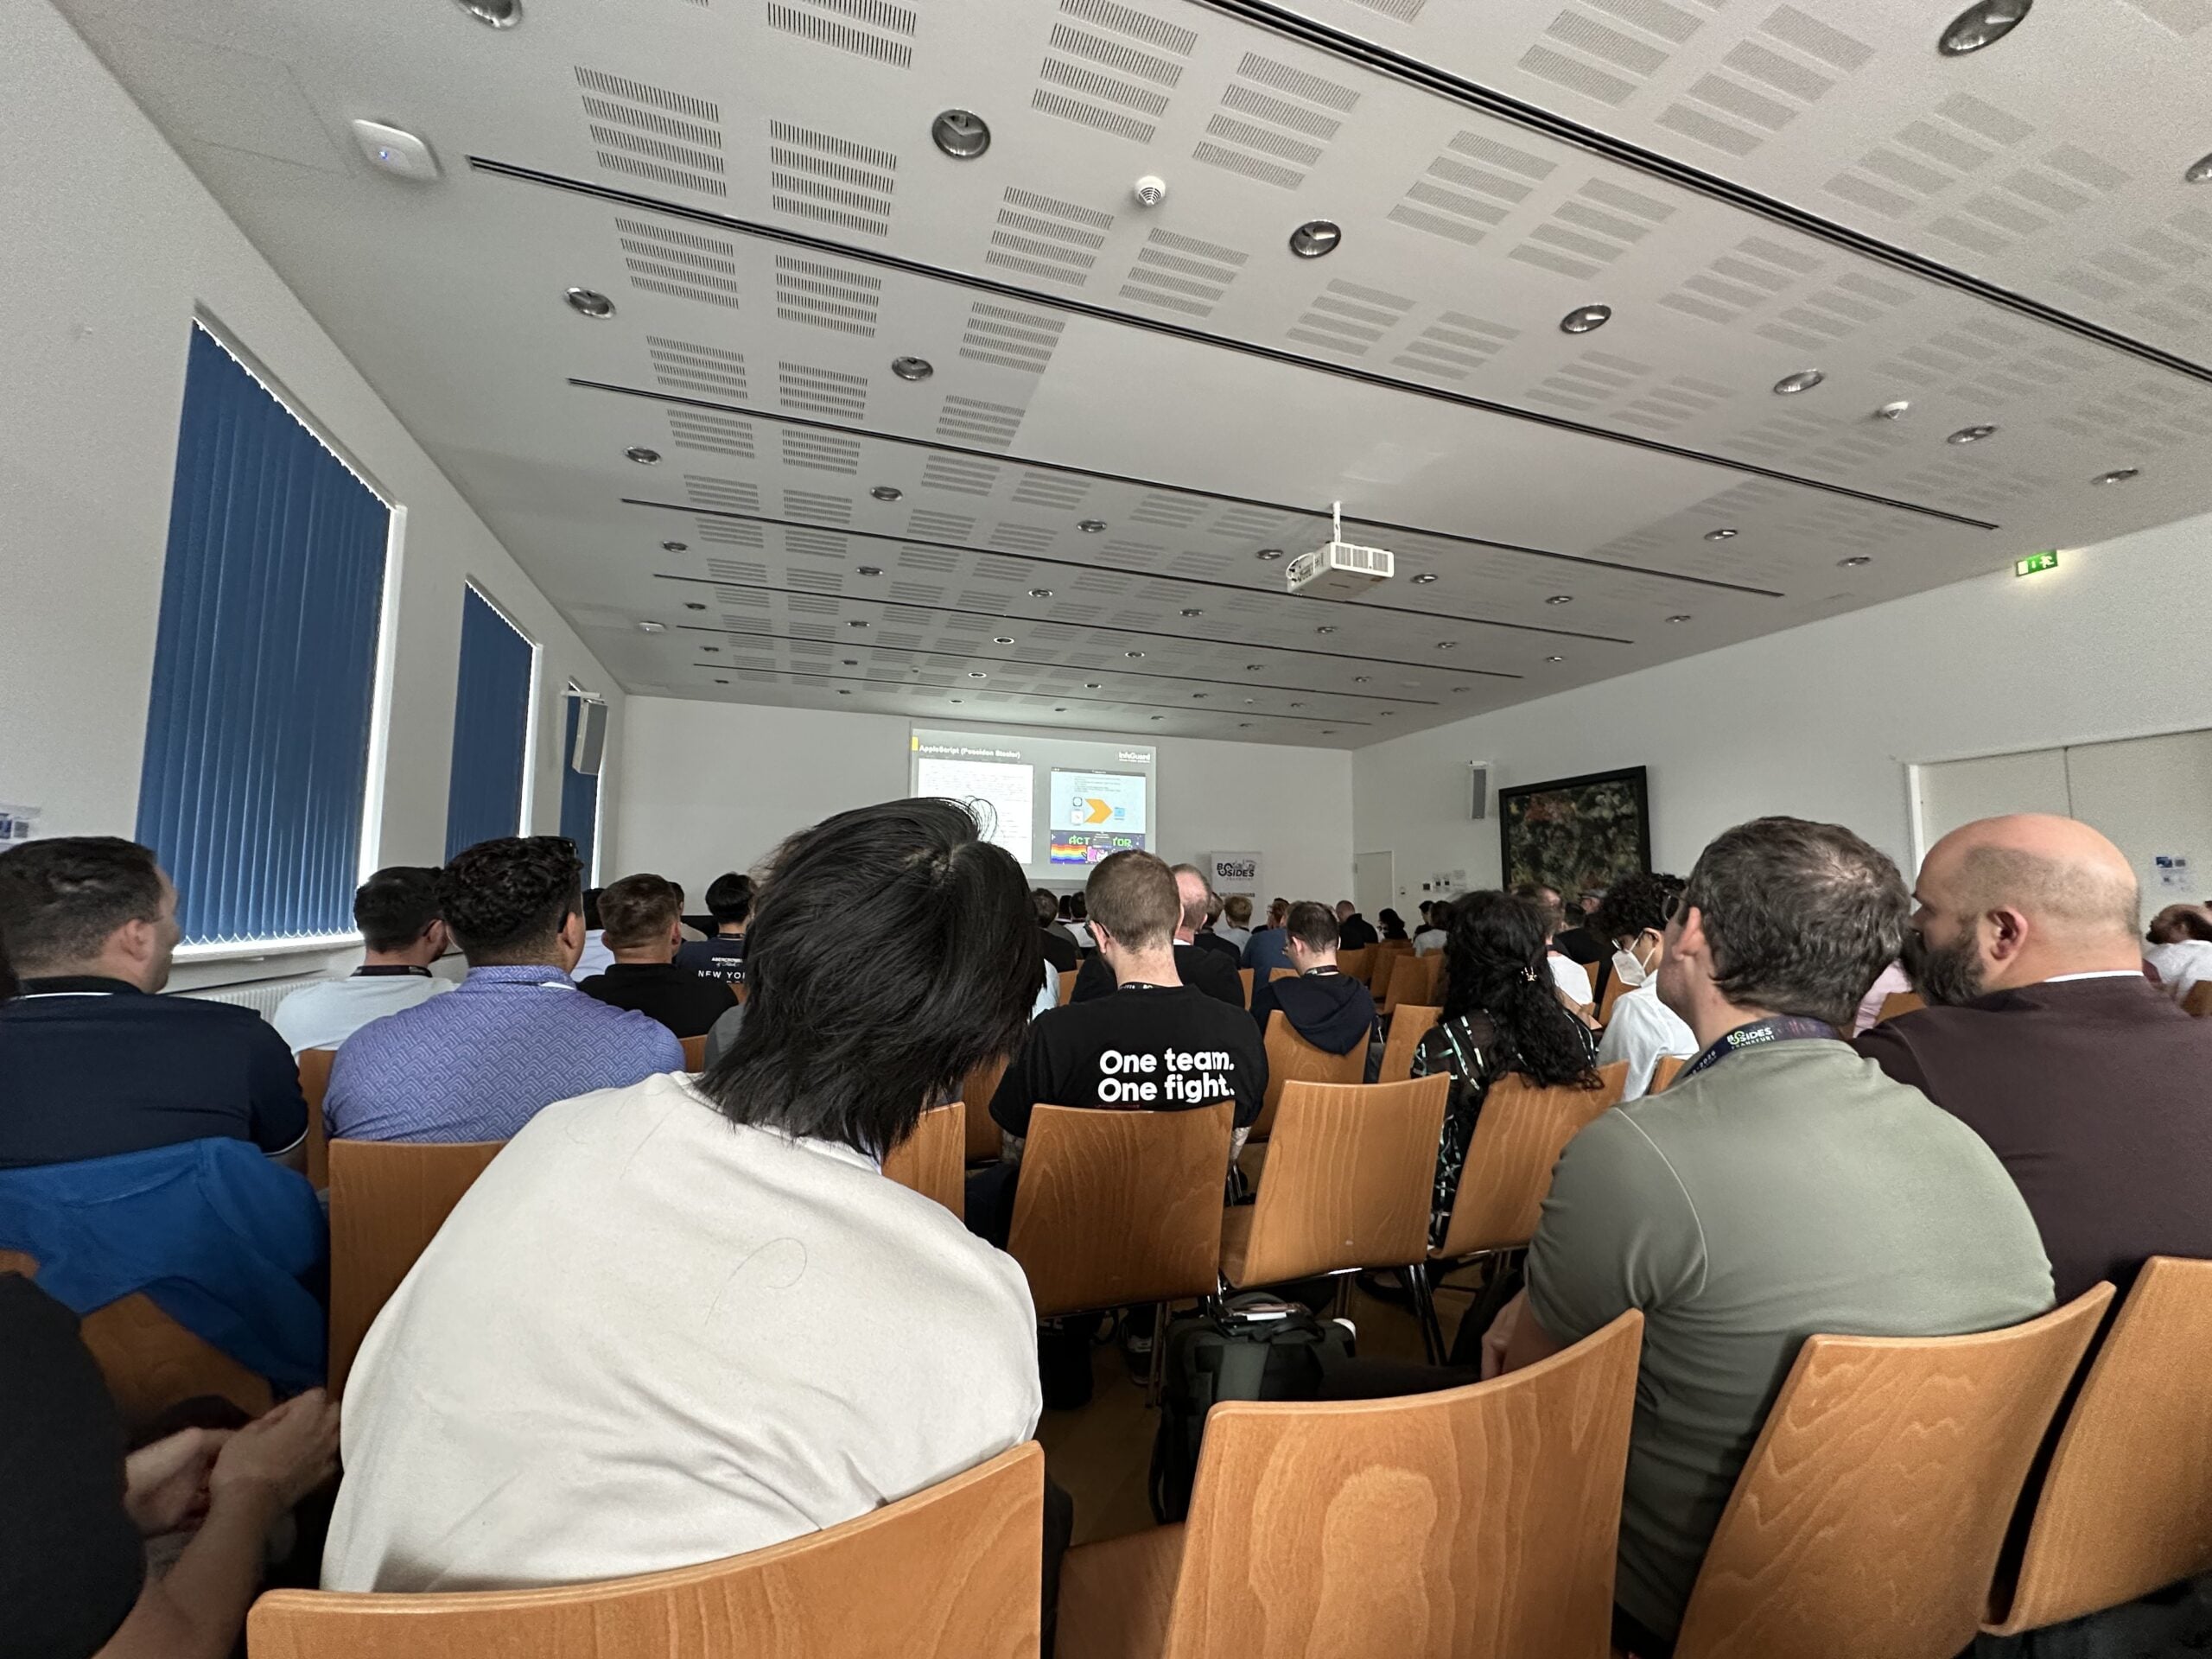
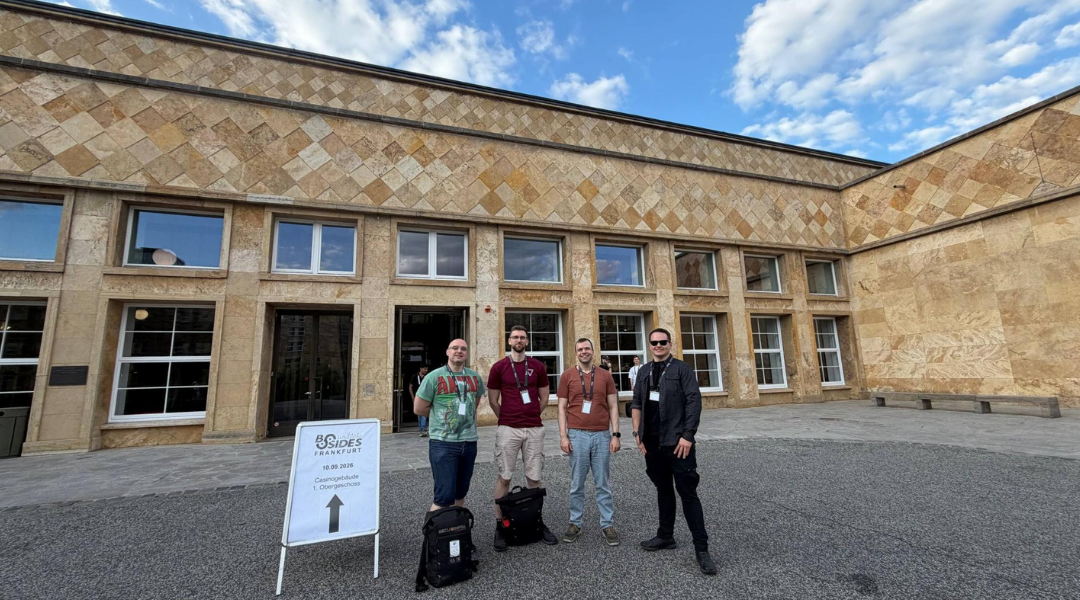
How do you uncover a cyberespionage attack that begins with a single phishing email? At BSides Frankfurt 2026, we addressed this question in a hands-on workshop with 25 participants. On September 10 and 11, the community conference at Goethe University Frankfurt brought security experts together to share knowledge. We were there with a fully booked workshop led by our DFIR specialist, Marius Genheimer.
Workshop Fully Booked: Hands-On APT Analysis
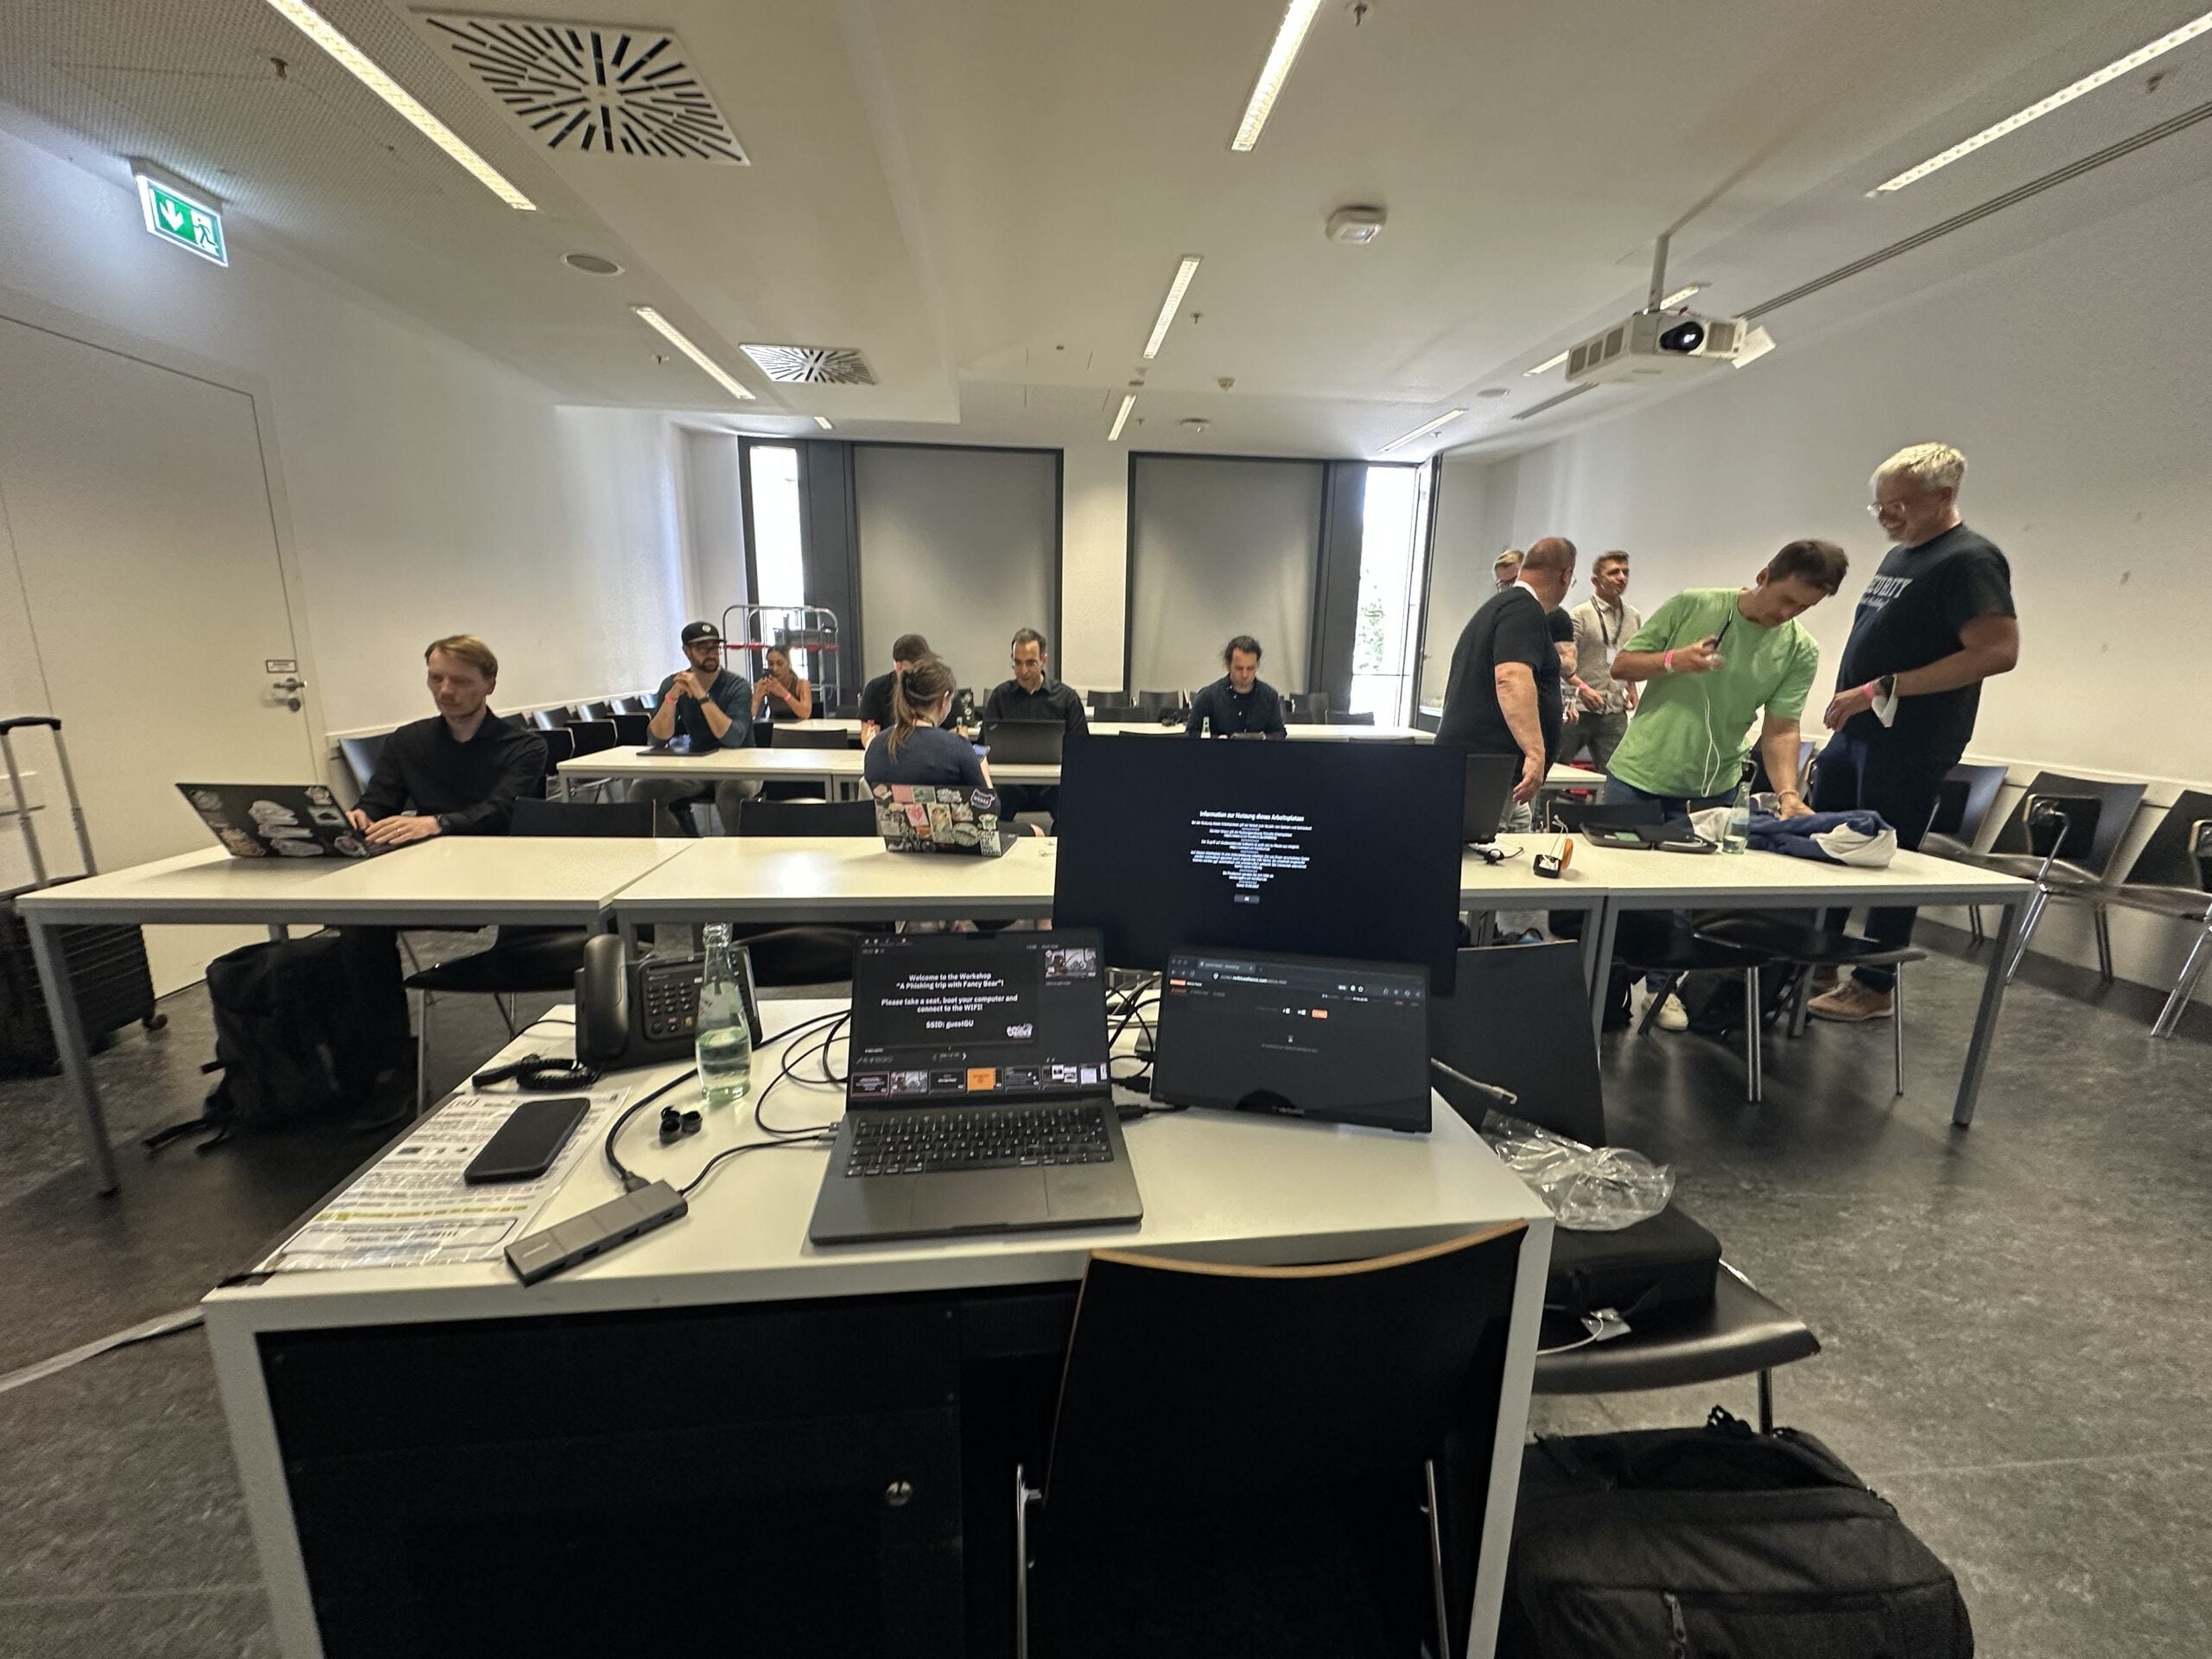
Under the title “A Phishing Trip with Fancy Bear – Let’s Analyze APT Malware Together!”, Marius walked the audience through the entire attack chain of a real-world case involving the Fancy Bear attack group, also known as APT28. This time, the session lasted four hours instead of the usual two.This allowed for more time to explore technical connections and delve deeply into the analysis on our own.
In five chapters that built upon one another, the session covered everything from the background of the attacker group to the delivery of the malware and the exploitation of a vulnerability, all the way to establishing a persistent presence in the system and command-and-control communication. Participants worked directly with real artifacts: phishing email headers, a rigged RTF document, malware samples, and a C2 implant.
The discussion then turned to specific details: How can relevant indicators be extracted from email headers? What role do manipulated Office documents and the CVE-2026-21509 vulnerability play? How do attackers use scheduled tasks, hide data in PNG files, or obfuscate strings using XOR and Base64? The analysis also covered the misuse of the open-source Covenant framework and trusted cloud services to disguise communications.
A specially developed interactive training platform accompanied the workshop. Quiz questions helped participants review their results and immediately see their progress. This made the workshop accessible even to less experienced participants. Using freely available open-source tools such as oletools and CyberChef, participants can also independently explore and deepen their understanding of the analytical methods taught.
Strong momentum from the security community
The rest of the program also impressed us with its diversity: presentations on hacking drones and electronic locks were complemented by sessions on Windows forensics and experiences with AI agents in the Security Operations Center. This combination of offensive and defensive perspectives made the event particularly exciting from a technical standpoint. The excellent organization provided the perfect setting for it.
We were particularly pleased with the positive feedback on the workshop. It serves as a strong incentive for us to make insights from the field of cyber defense understandable and practically accessible. Many thanks to the organizing team and all participants for a successful BSides Frankfurt 2026 and four intense hours of collaborative analysis!